• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

KB6NU's Ham Radio Blog

KB6NU's Ham Radio Blog
  • HOME
  • Study Guides
  • Teach a One-Day Tech Class
  • W8SRC Repeater Guide
  • Advertise
  • Hire Me

DEFCON

Does amateur radio need a DEFCON?

August 15, 2025 By Dan KB6NU 4 Comments

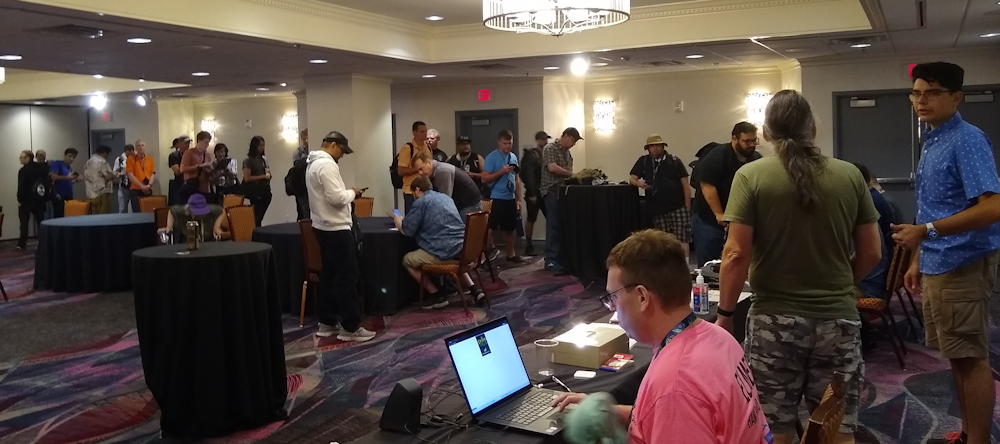
DEFCON logo.Last week, I taught my fourth one-day Tech class at DEFCON. DEFCON, as some of you may know, is one of the premiere hacker/cybersecurity conferences.

This year, I had 32 students in the class, and 30 passed the test that day, while the remaining two passed the next day after a little more study. 100% Yay!! The purpose of this post is, however, not to brag about my teaching prowess (well, okay, it is at least a little). Instead, I’m going to describe how DEFCON is organized and explore how we might adopt and adapt this model to amateur radio. And, in doing so, I’m going to compare and contrast DEFCON with the Dayton Hamvention.

The first comparison I’ll make is the number of attendees. Both events claim attendance somewhat north of 30,000. Hamvention is claiming an all-time high attendance of 36,814!

The second comparison I’ll make is the cost of admission. Hamvention costs between $25 and $30 to attend. DEFCON, on the other hand, cost $500 this year!

How does DEFCON get away with this? Well, first of all, DEFCON is more akin to a professional conference than a hobby gathering. While there are talks and activities that one would consider to be “hobby-oriented”—such as the Tech class I taught and the hidden transmitter hunts put on by the Ham Radio Village—the majority are geared towards the professional hacker and cybersecurity community. Overall, there were hundreds of talks and activities, wayyyyy more than you find at Dayton.

One of the reasons they are able to do this is they hold DEFCON at the Las Vegas Convention Center (LVCC), not a county fairground.  I don’t mean to criticize the Dayton Amateur Radio Association or the Greene County Expo Center, but just to compare the two venues. The LVCC is set up to handle the kind of event that DEFCON is. The Greene County Expo Center just doesn’t have the facilities to host more than four talks at a time.

The other interesting thing about DEFCON is its organization around “villages.” These villages are special-interest groups that focus on a particular activity. I already mentioned the Ham Radio Village (HRV). I haven’t counted how many other villages there were at DEFCON this year, but I’d say that there were at least a couple dozen. These included groups such as the Red Team and Blue Team villages, the Aerospace Village, the Automotive Village, the Social Engineering Village, the Biohacking Village, and many more.

Each of these villages is given the space to conduct their activities, which usually includes talks about the village’s subject matter. For example, the Ham Radio Village had talks about Meshtastic, AREDN, and how amateur radio might play a part in resisting a fascist government. To help ensure that the village had enough people to conduct all these activities, the DEFCON organizers give each village a number of free admissions to pass on to volunteers.

A DEFCON for ham radio

DEFCON is an incredibly cool experience. I’ve really only touched on a small part of it. Think how cool it would be if we had something similar for ham radio. Our villages could include a Digital Communications Village, some kind of Hardware Hacking Village (was there even a soldering skills workshop at Dayton this year?), a Software Hacking Village, an Antenna Hacking Village, and because I enjoy CW, a CW Village.

One thing that comes to mind—and this is just a partly-baked idea—is expanding the scope of QRP-ARCI’s Four Days in May. That might be asking too much of QRP-ARCI, though. Perhaps we could get groups like LICW or CWops to ramp up their activities at Dayton to form the CW Village.

One might think that the ARRL would be the perfect group to organize such an event. Unfortunately, they’re too busy alienating their members and playing silly political games to even consider doing such a thing. Instead of coming up with some original ideas of their own, I heard that they tried to take over Hamvention from DARA. That would have been a real disaster. Kudos to DARA for resisting that effort.

At any rate, I’d love to figure out how to do this. If you have any thoughts and would like to discuss this further, comment below or contact me directly.


Filed Under: Everything Else Tagged With: DEFCON

Amateur radio in the news: ARRL pays $1 million to hackers, hacker hams harassed, OM80SNP celebrates Slovak National Uprising

August 24, 2024 By Dan KB6NU 4 Comments

ARRL logoAccording to BleepingComputer.Com, “On Wednesday, ARRL revealed that it had indeed paid the attackers a [$1 million] ransom not to prevent stolen data from being leaked online but to obtain a decryption tool to restore systems impacted during the attack on the morning of May 15.”

A member bulletin detailing the situation was sent to members on Wednesday, August 21. The text of this bulletin can be read online.


Las Vegas hacker convention attendees complain of harassment by Resorts World staff

The hotel of Resorts World Las Vegas played host to many attendees of the convention this year, which ran from Thursday to Sunday at the Las Vegas Convention Center, and attendees of the cybersecurity conference complained that they were being treated like criminals by security.

In notices from Resorts World shared on social media, the casino-hotel warned guests of “room checks on all stay over rooms” in the block reserved for DEF CON attendees. Guests have also shared their own personal stories to social media, complaining of harassment by overzealous security staff with the intention to intimidate.

…

Some DEF CON attendees shared their negative experiences on forums, such as Hacker News. One, known by the username FickleRaptor, said security demanded their ID and threatened to have them arrested for trespassing. “The issue was that my colleague was one of the amateur radio VEs for the Ham Radio Village and happened to have his handheld with him,” they explained, adding that the guard was “aggressive, entitled, and arrogant.”

…read more


OM80SNP celebrates 80th anniversary of Slovak National Uprising

While listening to the August 21, 2024 podcast of Radio Slovakia International’s daily English show, I was surprised to hear a report on OM80SNP, a special event station commemorating the 80th anniversary of the Slovak National Uprising (Slovenské Národné Povstanie).

This station has been operating since August 1 and will continue through August 31, 2024.  A special QSL card is available.

Being Slovak-American, I wish I’d known about this sooner. I still have a chance to work them and get a QSL card, though.

Filed Under: Amateur Radio in the News, ARRL Tagged With: DEFCON, Slovakia

Why aren’t electronic badges more of a thing in #hamradio?

August 19, 2024 By Dan KB6NU 6 Comments

Electronic circuit board with LED screen and buttons.
DEF CON 32 electronic badge.

I attended DEF CON 32 a week or so ago, and like many “hacker” conferences, attendees got an electronic badge. This year’s badge was built around the new Raspberry PI microcontroller, the RP2350. It actually works like a GameBoy, and you can add games like you would a GameBoy. Here are a couple of videos that talk about the DEF CON 32 electronic badge:

  • https://www.youtube.com/watch?v=WWxjNNbiQ5Y
  • https://www.youtube.com/watch?v=tPrIO0fhikE

Some of the “villages” or special interest groups, such as the Aerospace Village created their own badges.

At DEF CON, I attended a talk by a fellow who’s created an open-source design—both hardware and software—upon which you can build a badge for your event. He calls his badge OpenTaxus, and you can find the documentation here.

Since these things are so popular at hacker conferences, I wonder why they aren’t more popular at amateur radio events? Is it because hams are just too cheap to buy something like this? Or, maybe, it’s because hams are just not as “creative” as hackers.

At any rate, I’m thinking about coming up with some kind of electronic badge for the 2025 Dayton Hamvention. If any of you have ideas for the badge—or would perhaps be interested in working on the badge hardware or software—let me know. If we are going to do a badge, it would probably be a good idea to get started on it now.

Filed Under: Hamfests, Microcontrollers Tagged With: badges, DEFCON, Hamvention

DEF CON 32: Another mind-blowing experience

August 13, 2024 By Dan KB6NU 4 Comments

I’m not a real fan of Las Vegas, but DEF CON is held in Las Vegas, so if I wanted to teach a one-day Tech class there, I just had to go. It was a fun, but tiring trip.

Getting there

I kinda made my travel arrangements last minute because the Ham Radio Village (HRV) folks weren’t sure that they were going to be able to secure a room for the class. That being the case, the only flight I was able to get was a late afternoon (4:50 pm) flight from Detroit. Same with the return. Instead of an early morning flight, I had to opt for the 1:15 pm flight, meaning that I wouldn’t get back to Detroit until after 8:00 pm. I managed to keep myself busy—there’s always something to do—but Wednesday and Sunday were mostly wasted.

I flew on Spirit. Enough said, I guess. It was packed. It was cheap, though, and the flight was direct to and from Detroit.

The flight out was fine. We even arrived about a half hour early. The return flight, however, was a real mess. We pushed back from the gate about 15 minutes late, but then, we sat on the tarmac for another hour and 45 minutes. I never did get a good explanation for what was happening. We arrived in Detroit an hour and a half late.

What a circus!

I stayed at Circus Circus because that’s what came up on booking.com as being close to the convention center. It was definitely close, but I really should have looked around some more. Circus Circus was built in the early 1960s, and it’s really showing its age. My room was clean enough, but the furniture was kind of banged up, there were spots where the wallpaper was peeling from the walls, and the air conditioner was very loud. Ugh.

There are many hotels around the convention center, and I think that if I shopped around more, I could have found a place with better rooms and a lower price. I took notes, and when I go back next year, I’ll be looking into those places as well.

Que rico!

Like everything in Las Vegas, the food is expensive. I lucked out, though, and found a place that was affordable, close to the Las Vegas Convention Center and my hotel, and delicious: Tacos El Gordo on Las Vegas Blvd.

Two tacos on a plate.
The food at Tacos El Gordo are worth the wait.

The tacos at Tacos El Gorda are the real deal. They advertise that the tacos are made Tijuna style, and you’d be hard pressed to find better tacos there. They’re made with handmade corn tortillas and homemade guacamole and salsas that are made from scratch daily.

When you enter Tacos El Gorda, you get into one of six lines, depending on the type of taco you want. On my first visit, I opted for the pork (adobada) tacos. In some places, they call this type of of taco a taco al pastor. The meat is sliced from a rotating spit, much like gyros is made, directly onto a tortilla. It really was excellent and only cost $4.12 per taco.

My second visit I decided to get a little more adventurous. I got into the line featuring organ meats, and after waiting in line for about a half hour, I ordered one taco de suadero (beef brisket—not so adventurous), one taco de cabeza (beef head—a little more adventurous), and one taco de buche (pork stomach—really adventurous). I liked the suadero and cabeza, but the buche not so much.

I’’m not really a gambler, but…

I’m not really a gambler, and in 2022 and 2023, I didn’t gamble a single cent. Many years ago, though, I bought some blackjack books and learned some basic strategy. So, this year, when I found a couple of blackjack machines in the Circus Circus casino that would accept $1 bets, I decided to give it a go.

Friday night, I fed a $20 bill into the machine and started playing. This machine was a little complicated in that it had a lot of side bets that you could make, such as whether you were dealt a pair or dealt 19+. I lost three of these sucker bets at a buck a pop before I figured that out.

Once I got that straight, I started playing plain old blackjack using the basic strategy. Using this strategy, your odds about 50-50, and that’s about how it played out. I pretty much broke even over the next half hour. Right at the end, I had a bit of a lucky streak, and when my total hit $20.80, I cashed out.

I say “cashed out,” but what the machine does is print out a ticket that you then have to take to a cashier to actually get cash. I thought that I might play a little again, so I just pocketed the ticket.

Saturday night, I did indeed decide to give it another go. There were only two machines that were working when I got to the casino, so I wandered around for a bit, visiting the circus stage and watching the hotel visitors try their luck at games on the midway. When I got back to the machines, one guy was just getting up, so I took his seat.

At first, I had a run of bad luck, and my total dropped to $15.30. But then, I got on a little bit of a roll, and built my total up to around $20 again. At that point, I played even with the machine for about 10-15 minutes. After a lucky streak bumped my total up to $25.50, I hit the cash out button again, and took the ticket to the cashier to collect my winnings.

My biggest class yet

The class went pretty well. Because we were only allowed to have 100 people in the room, HRV limited the pre-registration to 75. Despite the late start in publicizing the class, it filled up quickly. After getting all the pre-registered people in, they started accepting walk-ins, and we ended up with a class size of 90, making it the biggest class I’ve ever taught!

Since it was a bigger room than the one I taught in at HOPE, the setting wasn’t quite as intimate. The students had questions, but not as many as the HOPE class. Perhaps the size of the room had something to do with that. I’m not sure.

Unfortunately, we only had the room for seven hours, meaning that the students couldn’t test right away. Instead, they would have to take the test at DEF CON itself.

As a results, I’m not sure how many of the 90 students eventually passed the test. I know that over the course of the next couple of days I ran into several students who had passed the test. My guess is that a very high percentage did pass.

Mind-boggled

DEF CON is a truly amazing event. It’s a “hacking” conference, but the definition of hacking is about as broad as it can be. There were special interest groups, or “villages,” for a wide range of activities including hardware hacking, voting, lock picking (physical security), embedded systems, Internet of Things, and many more. And not only were there a couple of speaker tracks designed to appeal broadly, each village had their own series of talks. The enormity of it all just boggles my mind.

On Friday, I checked in at the Ham Radio Village and dropped off some of my No Nonsense business cards. I offered to help out, but they seemed to be all set, so I wandered off to experience the conference. I had a fun day attending talks, including a talk on open-source hardware for conference badges. I’ll be writing more about this later.

On Saturday, I updated my Ham Radio for Hackers slides and spoke on the topic in the Ham Radio Village. Like at HOPE, I had a really good turnout, and it was standing room only.

Immediately after, I went to hear a talk by Cory Doctorow in the main room, where he talked about the “enshittification” of the internet. If you haven’t’ heard this talk or read his articles about the subject, you should.

multi-colored bead bracelet
My wife, Silvia, loved this “friendship bracelet” that I made for her.

After that, I dropped in to the Women in Security and Privacy Village to make a “friendship bracelet” for my wife. I had been wracking my brain for something to bring home for her, and I knew the moment that I saw the program description that this was the right thing. Basically, the bracelets are simply a number of beads strung together on an elastic band. There were some letter beads, too, so I was able to spell out “SILVIA.” My wife loved it because as you can see, she spells her name a little differently than most Sylvias, and has always lamented the lack of things she could buy with her name on it. I scored a lot of points with Silvia when I got home, pulled it out of my bag, and slipped it on her wrist.

HRV Meetups?

After my talk on Saturday, a guy in his 30s (I’m guessing here) came up to me to talk about his experience with amateur radio. He had recently gone to a local amateur radio club meeting and was not received very warmly at all. He was so put off by the experience that he wasn’t sure whether to bother getting his license. Does that sound familiar?

I tried to explain that ham radio was a big hobby, and he unfortunately had just found the wrong crowd. I went on to say that not all hams were like that and encouraged him to get his ticket. Yesterday, I received an email from him that he had indeed passed the Tech test, and with the help of my study guide, also passed the General. That made me extremely happy.

Of course, he still needs to find his people. As I sympathized with him, it occurred to me that we need to create a way for hams like him to find other hams like him. I’m thinking of something along the lines of the 2600 meetups that used to happen around the country before Covid. Maybe we could even piggyback on existing 2600 meetups. I’ll be blogging about this soon, so if you have any ideas, I’d love to hear them.

Thanks to ARDC!

Thanks again to ARDC for funding this trip. The more I teach these classes, the more I’m convinced that we need to continue to reach out to this community. We need more people like the folks that attend DEF CON in amateur radio.

Filed Under: ARDC, Classes/Testing/Licensing Tagged With: DEFCON

An exhausting few days in Las Vegas

August 13, 2023 By Dan KB6NU 1 Comment

I just returned from Las Vegas yesterday, where I attended DEFCON and taught a one-day Tech class in the Ham Radio Village for the second year in a row. As it was last year, it was both exhilarating and exhausting. I arrived Wednesday afternoon, taught the class on Thursday, wandered about DEFCON on Friday, learned a few things, and left Saturday morning.

Students line up to register for the exam after my 2023 DEFCON one-day Tech class.

This year, there was another full house (pun intended) with 31 students in all. Unfortunately, only 24 passed the test. That’s a little lower than my usual pass rate, but come to find out that some of the students had never even looked at the study guide before the class. I know this because when I mentioned that I was following my study guide from front to back, several asked where they could get it.

I’m already thinking about next year. For example, I think with a little more publicity we could get 50 people to attend the class. Also, I probably should make up some slides to make up to show the students what resistors look like and what RF connectors look like. I usually have a goodie bag of components that I pass around for a local class, but it’s difficult to do that for a class somewhere other than Ann Arbor.

At lunch, an ICQPodcast listener joined me for lunch. That was nice. I told him that I was always surprised when people say they listen to us on the podcast. He replied that he was a relatively new ham, and that listening to the podcast helped him learn more about the community and become part of it. I hadn’t thought about that being one of our functions, but it’s something that I’m going to keep in mind on future episodes.

After the class, two study guide readers came up to me and thanked me for writing the study guides. One of them said that he used my study guides to pass all three tests. Now, he’s a VE with Ham Radio Village and giving back as well. How cool is that?

Hanging out at DEFCON

On Friday, I hung out at the conference and learned stuff. I learned a bit about quantum computing, how some people are using social media to chart the course of the war in Ukraine, and whether or not solid-state drives are actually more reliable than mechanical hard drives.

One of the other “villages” that I was really impressed with was the Hardware Hacking/Soldering Skills Village. They had at least a hundred people sitting at tables soldering and unsoldering things. Hamvention needs something like that.

While I’ll teach at DEFCON for as long as they’ll have me, I have never been a big fan of Las Vegas. I really have no desire at all to gamble anymore (I used to play a little blackjack), it’s incredibly hot in August (every day was over 100ºF), and the price for nearly everything is sky-high (I paid more than $20 for breakfast at a Dunkin Donuts!). Even so, it was packed to the gills. I was amazed that they get so many people there with such high temperatures and high prices.

Despite all that, DEFCON did get me pumped up about doing more hacking. For example, I’m going to look into purchasing a Xiegu X6100 and hacking on it. Apparently, the software runs on an internal Linux computer and can be user-modified. R1CBU has already hacked the X6100, adding features and improving the radio’s performance. I’m looking forward to learning more about this. I also have some other ideas, which I’ll be writing more about in the future.

UPDATE 8/15/23

I got this very nice email today:

Hi Dan,

Thank you for teaching your class @ DefCon! I was lucky enough to snag a spot at the very last minute; I got a lot out of the class but, since I had no prior knowledge of/experience with the subject and the exam was being offering for the duration of the con, I decided to hold off until I’d had a chance to review the material.

That said, I’m happy to share that I took & passed the exam on Sunday after re-reading your guide and taking a practice test.

So, thank you again for piquing my interest in ham radio & making it so accessible — I hadn’t expected to leave Las Vegas a licensed amateur radio technician!

I’ve since downloaded your “21 Things to do After” guide and look forward to getting started with my first radio.. : )

How cool is that? That bumps up my pass rate a little more  :)

Filed Under: Computers, Gear/Gadgets, Software-Defined Radio (SDR) Tagged With: DEFCON, hacking, Las Vegas

Hack the ARRL?

August 6, 2023 By Dan KB6NU 4 Comments

This week, I’m headed to DEFCON, which is arguably the premiere hacking conference in the world. DEFCON hosts a a number of special interest groups they call “villages,” which organize their own sub-conferences on topics ranging from artificial intelligence to voting. One of those villages is the Ham Radio Village, and as I did last year, I’ll be teaching a one-day Tech class in the Ham Radio Village on Thursday, August 10.

So, what does this have to do with the ARRL? Well, one of the more popular amateur radio sub-hobbies is to complain about the ARRL. I won’t list them all here—my website account doesn’t have unlimited disk storage—but I think that most of you agree that there are more than a few complaints out there.

Well, part of the hacker ethos is to not just complain about things, but to do something about it. The Wikipedia entry on hacker culture puts it this way, “[hackers enjoy] the intellectual challenge of creatively overcoming the limitations of software systems or electronic hardware (mostly digital electronics), to achieve novel and clever outcomes.” It seems to me that we could creatively overcome some of the limitations of the ARRL, i.e. hack the ARRL, if we put our minds to it.

I think that Parks on the Air (POTA) is a good example of this. The ARRL actually gave birth to POTA with their year-long National Parks on the Air program in 2016, which celebrated the 100th anniversary of the U.S. National Park System. It was a very popular activity, but the ARRL dropped it like a hot potato once the year was over.

Fortunately for us, a dedicated group of ham hackers stepped up and created the current POTA program. POTA is wildly popular and has been a real boon to amateur radio.

Get your hacking hats on

So, what else can be hacked? One thing that I can think of off the top of my head is Logbook of the World. At one time, there was talk about making it a more real-time system. I’m not sure whatever happened to that project, but my guess is that the programming was a lot more complicated than originally anticipated, and it got put on the back burner.

Another possible ARRL hack would be to do something about the ARRL’s digital magazines. This hack is particularly needed now that fewer and fewer members are going to be getting the print versions of QST, QEX, and the National Contest Journal. Making the information more easily accessible I think would end up being beneficial for the ARRL as well as ham radio in general.

Can you hack a hamfest?

This isn’t strictly an ARRL thing, but one aspect of ham radio that I would love to see hacked is hamfests. On Mastodon today, someone wrote:

Researching local hamfests, and they’re still such an old man thing. 7 am open gates. Grange fair. Fire house. Greasy breakfast cart. Noon close.

Can we get like a 3 pm start time at a farmer’s market with snacks, kombucha, and chiptune DJ?

My reply was, “There’s nothing that I know of that stopping anyone from starting something new.” It wouldn’t be easy to do, but life’s not easy, right? Hackers take on difficult challenges because they are difficult, don’t they? So, let’s get to it.

Filed Under: ARRL Tagged With: DEFCON, hacking/making

From my inbox: how transistors work, texting device, DEFCON talks

March 18, 2022 By Dan KB6NU Leave a Comment

Understanding Basic Electronics

The Long Island CW Club has turned into much more than a place for hams to learn Morse Code. It really is an online amateur radio club. Their Zoom rooms host talks on a wide variety of topics, and their mailing list has become a forum for less experienced hams to seek out the advice of those who, shall we say, have been in the hobby for a while.

A recent thread, Understanding Basic Electronics, caught my eye. It has a number or resources to help the new ham learn electronics. Of those, there’s one I really like, How Transistors Work – A Simple Explanation. It has explanations for how both bipolar junction transistors and field-effect transistors (FETs) work.


Chatter uses LoRa to send encrypted texts

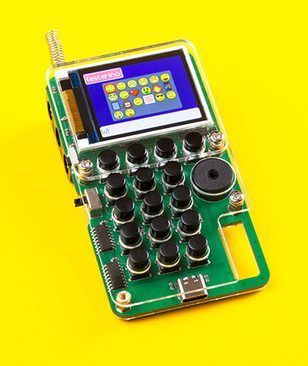
Chatter is an amusing little device that uses LoRa to send encrypted text messages. I’ve often thought that a device like this, but operating on the amateur radio bands, would be a killer app for amateur radio.

This particular device is kind of expensive at $132. Not only that, it comes as a kit that you have to put together yourself. Both those being the case, I don’t see this becoming a big seller. It is amusing, though.

I haven’t checked in with the Ham Messenger developer lately, so I don’t know how that project is going. For folks with a license, though, I’d still recommend that that is the way to go. Of course, since Ham Messenger uses amateur radio frequencies, the messages can’t be encrypted. It seems a bit silly that you can encrypt using an unlicensed service, while you can’t with amateur radio, but them’s the rules.


From Southgate ARC:

Talks from the Ham Radio Village at DEF CON 29 released

The amateur radio talks given in the Ham Radio Village at last year’s DEF CON 29 event are now available on YouTube. The talks include:

  • An Introduction to RF Test Equipment by Kurtis Kopf K6GG
  • Amateur Radio Mesh Networking by Tyler Gardner KI7ODK
  • Spectrum Coordination for Amateur Radio by Bryan Fields W9CR
  • Getting started with low power/long distance comms (QRP) by Eric Escobar W6WD
  • How to Contact the ISS with a $30 Radio by Gregg Horton K6XSS

Watch the talks on the DEFCON YouTube channel.

Filed Under: Electronics Theory, Gear/Gadgets, On the Internet, Videos Tagged With: DEFCON, Long Island CW Club, LoRa, texting

Primary Sidebar

No Nonsense Technician Class License Study Guide (for tests given between July 2026 and June 2030)

New No Nonsense Technican Class Study Guide now available!

The 2026 version of my Tech Class study guide is now available, and as always, the PDF version is FREE!. The ePub version costs $11.97, and a Kindle version and paperback version will be available on Amazon shortly.

Click here to get all of my "No Nonsense" study guides.

Also available: The CW Geek's Guide to Having Fun with Morse Code

W5SWL.Com
Retevis Ailunce H1 DMR Radio
DXpander: Cobweb antennas, Laser Cutting

You’ve got mail!

Enter your email address below and get an email every time I publish a new post.

Email


I frequently teach classes to help newcomers get their licenses. The next class will take place on Saturday, October 10, 2026 on the University of Michigan campus. Click here for more information.

If you can't make the class, subscribe to the mailing list to be notified of when the next class will be held.

You can always download my free study guide, and if you have any questions about the classes, or amateur radio in general, please feel free to email me directly.

Support KB6NU.Com

Donate $7.30 and get two of these cool stickers. Measuring 4.25-in. W by 2.75-in. H, it's perfect for your car, your shack, or wherever!

Contact me

If you have a question or comment about one of my blog posts, or a question about any of the material in my study guides, or just a question about ham radio in general, you can email me at [email protected].

Blogs You Should Also Read

  • AE5X: A CW-centric blog from Kingswood, Texas
  • K0LWC Blog
  • LA3ZA Ham Radio Blog
  • Little Radios, Big Fun – WB3GCK
  • Mr. Vacuum Tube's Blog
  • Radio Artisan – K3NG
  • The K0NR Weblog
  • VE3WDM's QRP Ham Radio Blog
  • W2LJ’s Blog

Ham Radio Websites

  • Dashtoons – The Hammin' Comedy by Jeff K1NSS

Podcasts

  • ICQ Podcast
  • Linux in the Ham Schack
  • No Nonsense Amateur Radio Podcast
  • Resonant Frequency Amateur Radio Podcast

Recent Comments

  • Bulin 47 AI on ICQPodcast Episode 485 – World Cup Special Event Station
  • Jesse Alexander on What do you think of this artwork for the ham radio EMF Explorer
  • CADProps on My first go at 3D printing not quite a success
  • Dan KB6NU on A Media Guide to Amateur Radio
  • Steve Stroh N8GNJ on A Media Guide to Amateur Radio

Meta

  • Log in
  • Entries feed
  • Comments feed
  • WordPress.org

Footer

Copyright © 2026 Daniel M. Romanchik, KB6NU · Log in